API integration planning checklist for business websites and apps
API integration planning is about making business systems agree on data and handling the times when they do not. Connecting an endpoint is usually easier than deciding record ownership, retries, duplicates and recovery. Before integrating a website, store, CRM or custom application, define the information that moves, what confirms success and who resolves a failed transfer. This guide turns those decisions into a testable scope.
Key takeaways
- Assign one source of truth for each important field or business state.
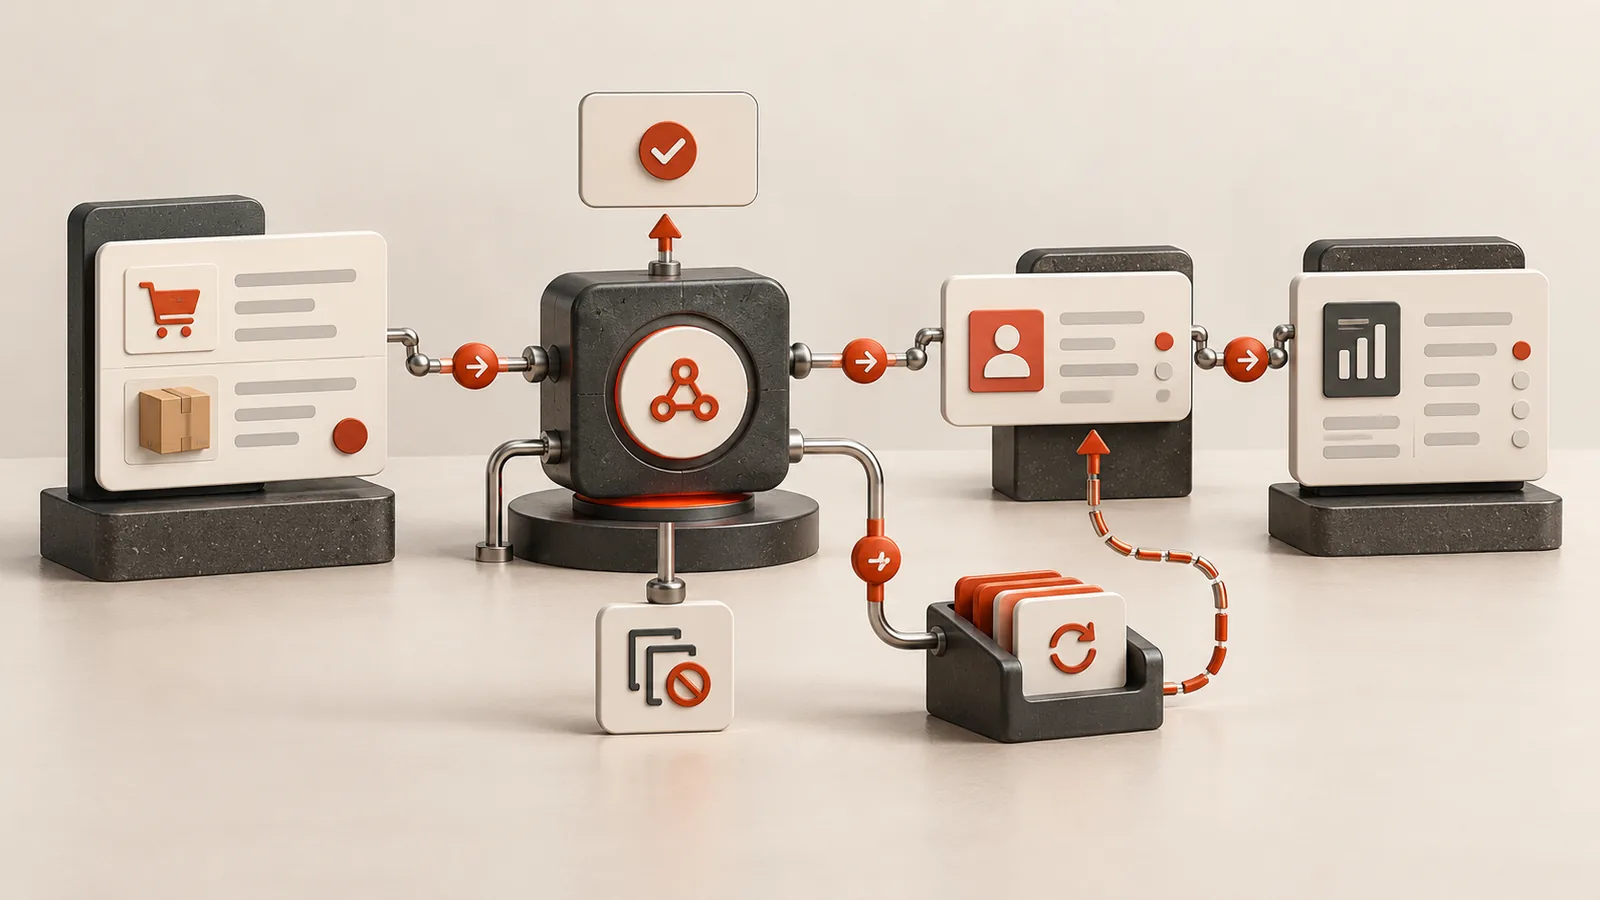
- Plan duplicate handling, retries and recovery before the happy-path demo.
- Give staff a visible integration status and a controlled way to resolve failures.
Start with the business event and record ownership
Describe the event that starts the integration: a paid order, an accepted enquiry, a stock adjustment or an approved client request. Then name the record that should be created or changed in the receiving system. Avoid a vague requirement to keep everything in sync. It hides disagreements about which system is allowed to update a field and what should happen when two changes conflict.
Create a small data contract. Record identifiers, required fields, formats, optional values and the meaning of each status. Decide how an existing record is matched and what happens when a lookup fails. Include the person who uses the receiving system in this discussion. A technically valid payload can still produce an operationally incorrect record if the business meaning has not been agreed.
| Decision | Question to resolve | Failure to test |
|---|---|---|
| Identity | Which stable ID links the records? | The same event is delivered twice |
| Ownership | Which system may change this field? | Conflicting edits occur |
| Timing | When must the update become visible? | The destination is unavailable |
| Validation | What data is mandatory and accepted? | A required value is missing or invalid |
| Recovery | Who can inspect and retry a failure? | An update stops between two systems |
- Map each event to a specific destination action.
- Document identifiers, field ownership and the meaning of statuses.
Verify access, limits and a safe test environment
Confirm that the relevant API operations are available to the account and that the provider supports the workflow you need. Check the current documentation rather than relying on an example written for another version. Identify authentication requirements, documented limits and how credentials can be renewed or revoked. Business secrets belong in the appropriate server-side environment, not in downloadable browser code.
Use test accounts and sample records where the provider supports them. Agree which real data may be used during diagnosis and avoid copying entire customer datasets just to prove a connection. Record external dependencies that affect the schedule, such as account approval or provider support. A small technical investigation should establish whether the required operations work before the project commits to a detailed implementation estimate.
- Prove the required read and write operations before full development.
- Record provider limits, account ownership and credential maintenance.
Design for repetition and interruption
An external event can arrive again after the first request appeared to fail. Decide how the receiver recognises an operation it has already completed. Use the provider's stable event or business identifiers where suitable, and make the destination update safe to repeat. Stripe's webhook guidance is one practical reference for duplicate delivery and event-order considerations.
Separate a temporary interruption from a permanent data problem. A brief outage may be retried; an invalid account reference needs correction. Define a bounded retry policy, a place to inspect unresolved items and a way to prevent retries from overwhelming the destination. If multiple steps must happen, record enough progress to tell which step completed. Do not present a successful integration state merely because the initial request was sent.
- Test repeated events without creating duplicate business records.
- Distinguish retryable interruptions from failures that need human correction.
Validate authenticity and restrict what the connection can do
Treat incoming requests as untrusted until the appropriate provider verification has succeeded. Validate required data and enforce the permissions needed for the operation. Follow the provider's documented signature or authentication process rather than assuming that an obscure URL makes a webhook private. Keep credentials scoped to the required capabilities and define how they will be rotated.
Plan operational logs around useful identifiers and outcomes. A support person may need to know which order failed and why, but that does not require recording every credential or personal field in plain text. Decide what can be viewed, who can view it and when diagnostic information is removed. Security and troubleshooting should be designed together so recovery does not depend on exposing more data than necessary.
- Verify provider requests and validate the fields used by the application.
- Keep secrets and unnecessary personal information out of routine logs.
Accept the integration with business-level scenarios
Test a normal event, a duplicate, an invalid value, an expired credential and a temporary destination outage. Add scenarios specific to the workflow, such as a cancelled order after an earlier successful transfer. Verify the final business record in each system rather than stopping at a successful HTTP response. Document how staff inspect and recover a failed item.
Handover should include the data contract, provider accounts, deployment configuration, monitoring and recovery instructions. Agree who reviews provider changes and who owns the integration when either connected application is updated. A reliable API integration is an operating process supported by code, not a one-time connection that can be forgotten once the demonstration works. Scope that responsibility explicitly so the integration stays useful after launch.
- Include negative and repeated-event scenarios in acceptance.
- Assign ownership of alerts, provider changes and recovery procedures.
Sources and further reading
Primary documentation for the platform-specific details discussed in this article. The planning examples above are illustrative requirements, rather than client case studies.
Need your website and business systems to work together?
Tell me which event should move between which systems, and what currently goes wrong. I can help define the data contract, recovery behaviour and implementation scope.
Discuss a projectFrequently asked questions
Practical answers to help you plan the next step.
Complex data rules, weak documentation, authentication limits, unreliable third-party systems and unclear ownership make integrations harder.
Only when the workflow needs it. Some systems work better with scheduled syncs because they are more reliable and easier to recover.
Yes. CRMs, payments, booking systems, email platforms and internal databases can often be connected when the workflow is clear.